Credentials and outbound endpoints
Review Named Credentials, External Credentials and outbound endpoints with relevant retained configuration and security findings.
Security Observatory by Fortmilo
Security Observatory turns observed application, OAuth, credential and endpoint evidence into durable records with ownership, purpose and review context — and keeps the evidence behind each one.
Currently in sandbox validation. Not yet available for public installation.
Prefer email? info@fortmilo.co.uk
Application and integration governance
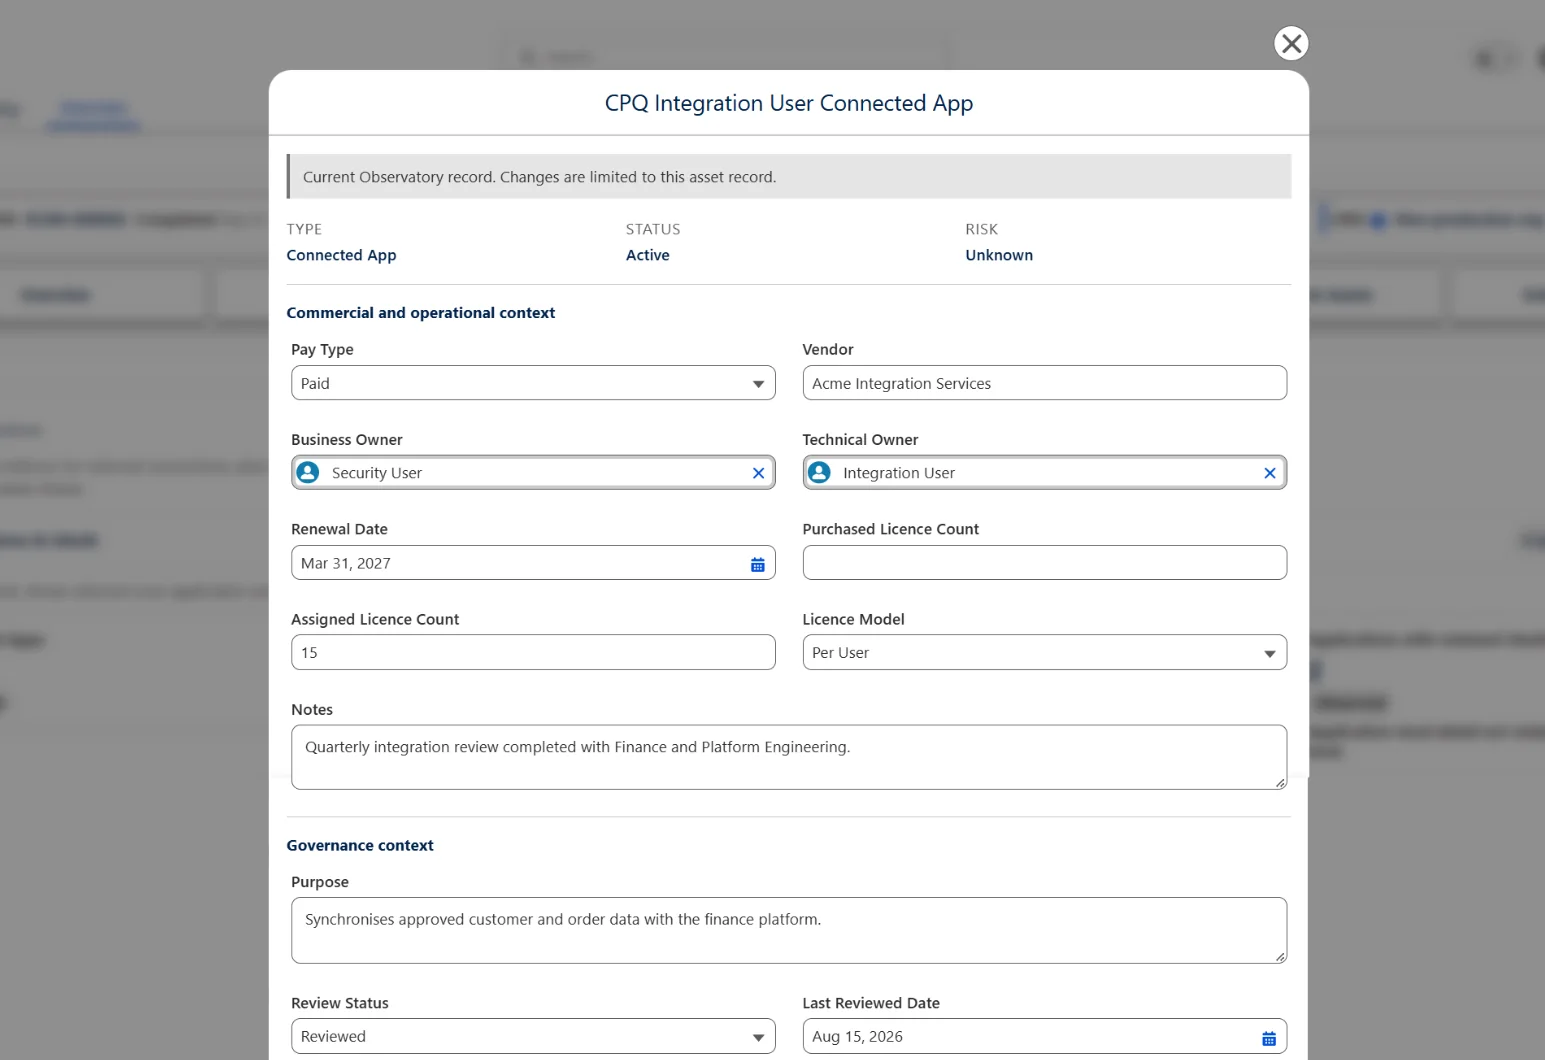
Supported observed applications and integrations can become durable governed records that remain useful across rescans.
Where supported, a record can hold a business owner, technical owner, vendor, purpose, business context, review status, last-reviewed date and relevant renewal or review context. Human-entered governance context is preserved while source provenance, linked OAuth context and associated findings keep the record traceable; fields are completed through review rather than assumed from the source.
The independent Security Benchmark for Salesforce (SBS) calls for authoritative inventories, documented ownership, justification and review evidence across key Salesforce security areas; Security Observatory provides a governed place for that context alongside the technical evidence.
Integration surface
Security Observatory reviews supported integration configuration without claiming to discover every integration.
Review Named Credentials, External Credentials and outbound endpoints with relevant retained configuration and security findings.
Bring Remote Site Settings, CSP Trusted Sites and the CORS allowlist into the same bounded review, with certificates available as supporting evidence where relevant.
Review supported Salesforce Sites and Experience Cloud evidence alongside the applications and connections that give it context.
OAuth correlation
Correlate retained OAuth authorisation evidence with the observed application, supported user state, stale or non-use evidence when available, governed application context and associated findings. Inactive or frozen user context remains explicit where the source supports it.
An authorisation record does not prove a credential currently works, and Security Observatory never probes it.
No tokens · No session IDs · No secrets · No certificate bodies · No raw IPs
This describes evidence retained, displayed and exported by Security Observatory.
Complementary role
Salesforce Security Center provides native security posture monitoring and security management for Salesforce orgs. Security Observatory is built around a different job: recording the applications, integrations and access that can reach your org, giving them accountable review context and keeping the evidence behind each entry. It is designed to complement Salesforce's native security capabilities, not replace them.
Questions to bring into focus
Evidence integrity
Conclusions retain their source and evidence context. When evidence is unavailable, it remains unavailable and must not silently become zero.
Why the Observatory
It gives supported applications and integrations durable accountability, connects OAuth evidence to user and application context, and brings credential, endpoint and public-surface evidence into the same review.
Each conclusion stays traceable to retained evidence and bounded by what the source could establish.
Supporting coverage
Supporting breadth remains evidence-bounded and secondary to the governed application and integration record.
Health Check configuration evidence, Connected Applications, certificates and sensitive administrative changes. Deeper Health Check and Tooling evidence requires subscriber self-callout setup.
User posture, login and failed-login evidence, sessions, API-enabled access and selected powerful or data-exposure permissions.
Licence capacity and bounded assignment evidence with explicit capture and completeness limits.
Next steps
Explore the bounded V1 scope, or request access when it becomes available.
Email: info@fortmilo.co.uk