Credential configuration
Keep supported Named Credential and External Credential evidence connected to the application or integration under review.
Security Observatory overview
Create accountable records for supported observed applications and integrations, connect them to OAuth and user context, and retain the evidence behind each review.
Currently in sandbox validation. Not yet available for public installation.
Email: info@fortmilo.co.uk
Governed application lifecycle
Security Observatory maintains durable governed application records from supported evidence sources. Records can hold a business owner, technical owner, vendor, purpose, business context, review status, last-reviewed date and relevant renewal or review context, while retaining links to source provenance, OAuth usage and associated findings. Human-entered governance context is preserved across rescans where the current record model supports it.
Credentials and endpoints
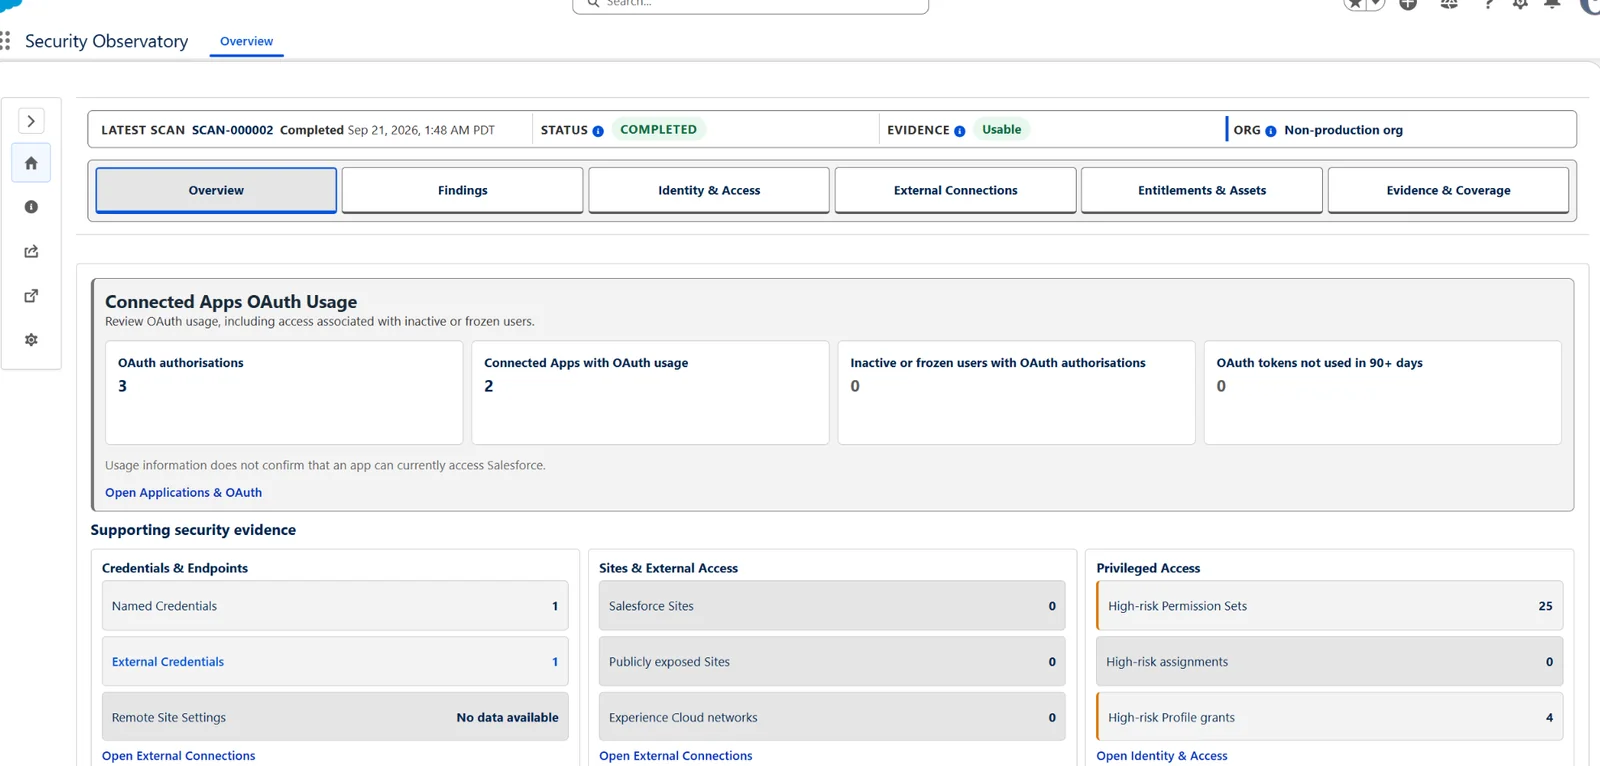
Review Named Credentials, External Credentials and outbound endpoints alongside Remote Site Settings, CSP Trusted Sites, the CORS allowlist and certificates as supporting evidence where relevant.
Keep supported Named Credential and External Credential evidence connected to the application or integration under review.
Review supported endpoint configuration and related findings without claiming comprehensive integration discovery.
Retain source provenance and link relevant findings back to the governed record.
OAuth context
Correlate the application, retained OAuth authorisation evidence, supported user state, stale or non-use evidence when available, governed context and associated findings.
An authorisation record does not prove a credential currently works, and Security Observatory never probes it.
Public exposure
Supported Salesforce Sites and Experience Cloud evidence brings public-surface context into the same review as applications, connections and findings. Conclusions remain bounded to the evidence sources the scan could assess.
Independent governance rationale
The Security Benchmark for Salesforce (SBS) is an independent project, not a Salesforce product or a Fortmilo benchmark, and it is not endorsed or supported by Salesforce. Security Observatory uses version-bound control references as pointers to retained evidence, not as statements that a control is satisfied, compliant, certified, secure or passed. Where human judgement is required or a source is unsupported, the review retains Manual Required or Not Covered as applicable.
SBS material is attributed under CC BY-SA 4.0; Security Observatory identifies the referenced source/version and any mapping modifications.
Evidence integrity
Source provenance, observed-zero, unavailable, incomplete and intentionally unretained evidence remain distinct so a review does not overstate what the scan established.
Collection and retention occur inside the subscriber Salesforce organisation. The authenticated browser prepares allow-listed CSV content; downloading creates a separate file boundary outside Salesforce.
No tokens · No session IDs · No secrets · No certificate bodies · No raw IPs
This describes evidence retained, displayed and exported by Security Observatory.
Product guide
Each area states what the Observatory surfaces and how far the evidence goes.
Triage retained risk evidence and open safe detail.
Open Findings →Review governed applications, OAuth, credentials, endpoints and public Salesforce surfaces.
Open External Connections →Review supported users, session exposure, login evidence and selected powerful access.
Open Identity & Access →Review licence capacity, bounded assignment evidence and governed application records.
Open Entitlements & Assets →Review provenance, source availability, completeness and bounded retained history.
Open Evidence & Coverage →Supporting coverage
Supporting review areas cover active, inactive, frozen, administrative and stale-login users; sessions and failed-login evidence; API Enabled, delegated administration and login access; selected powerful permissions; and bounded licence evidence.
Scope boundary
V1 scope current as of 21 September 2026.
PackageLicense record. This is not a complete installed-package inventory.Paid extensions for continuous monitoring, longer evidence history and estate-wide governance are under consideration for a later release.
Request access
Security Observatory is not yet available for public installation. Contact Fortmilo to request access when it becomes available.
Email: info@fortmilo.co.uk