Named Credentials
Review retained identity, endpoint and configuration context without retaining credential values.
External Connections
Connect supported OAuth, governed application, credential, endpoint and public-surface evidence without retaining or testing credential values.
OAuth exposure
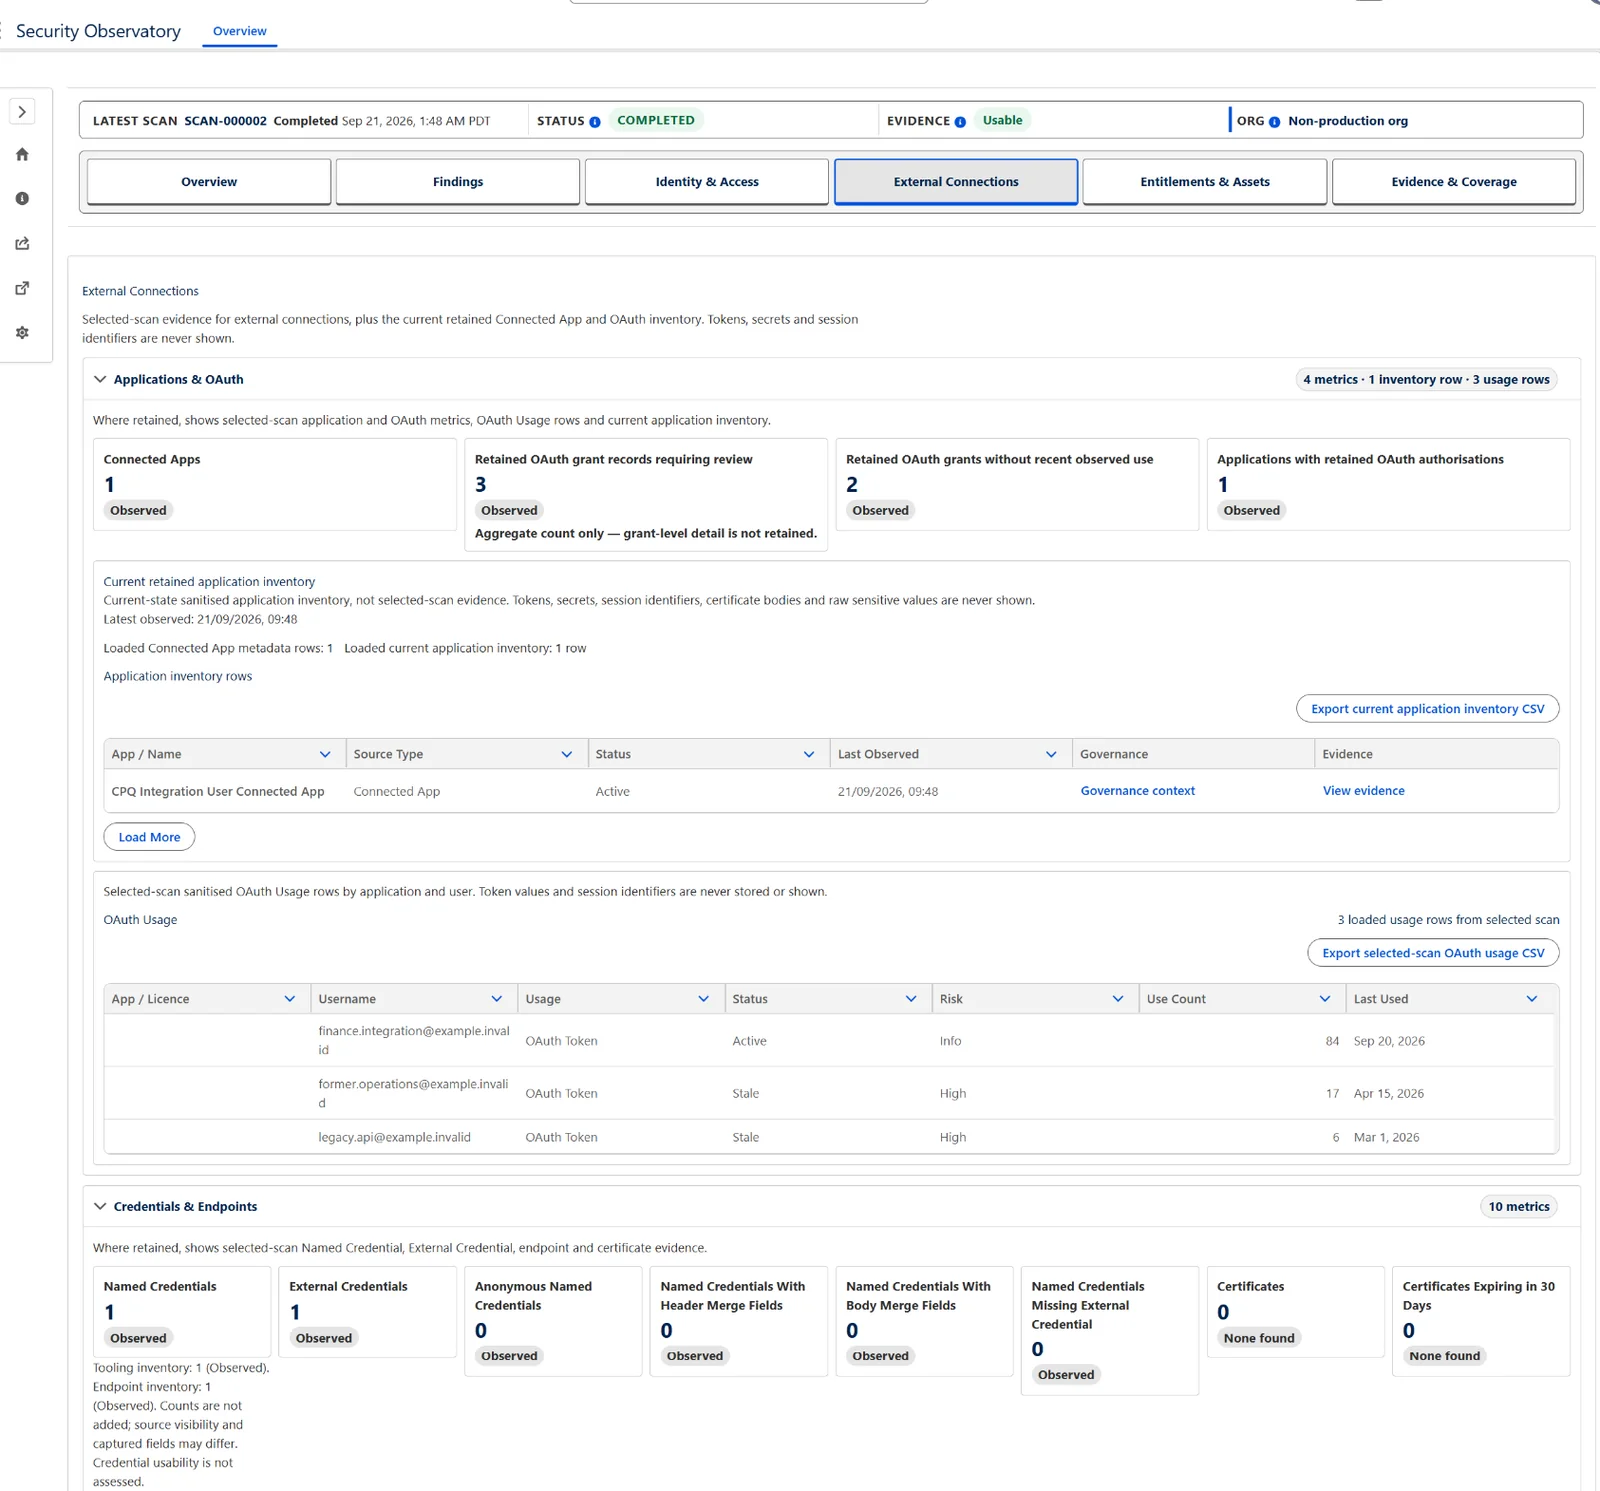
Correlate the observed application, retained OAuth authorisation evidence, supported user state, stale or non-use evidence when available, governed application context and associated findings. Inactive or frozen-user context remains visible where the OAuth source supports it.
An authorisation record does not prove a credential currently works, and Security Observatory never probes it.
Governed application records
Supported observed applications and integrations can be created or reconciled as durable governed records. Where supported, reviewers can retain business and technical ownership, vendor, purpose, business context, review status, last-reviewed date and relevant renewal or review context.
Human-entered governance context is preserved while source provenance, linked OAuth context and associated findings keep the record traceable. No claim is made that every integration source is discovered or that governance fields arrive populated.
Credentials
Bring supported credential configuration into the same review as the application and its endpoints.
Review retained identity, endpoint and configuration context without retaining credential values.
Review supported External Credential association and principal context alongside the related Named Credential.
Keep current scanner-supported credential and endpoint findings linked to the source evidence and governed application, with limitations stated where evidence is unavailable.
Endpoint and egress configuration
Security Observatory reviews supported Remote Site Settings, CSP Trusted Sites, the CORS allowlist and outbound endpoints. Certificates provide supporting evidence where relevant; this is a bounded configuration review, not a claim of comprehensive integration discovery.
Review supported allowlisted remote destinations and their retained source context.
Review supported CSP Trusted Sites and CORS allowlist entries as distinct egress and browser-access configuration surfaces.
Connect outbound endpoint evidence and relevant certificate context to findings where supported.
Public Salesforce surfaces
Bring supported Salesforce Sites and Experience Cloud evidence into the application and integration review. Guest or public context is presented only where the assessed source supports it, and unavailable source evidence remains unavailable.
Scope boundary: External Client App inventory is not included in V1. Some Tooling API evidence requires subscriber completion of self-callout setup.